Researchers found a new iPhone spyware variant that can remotely extract cryptocurrency wallet data and sensitive credentials from compromised devices.
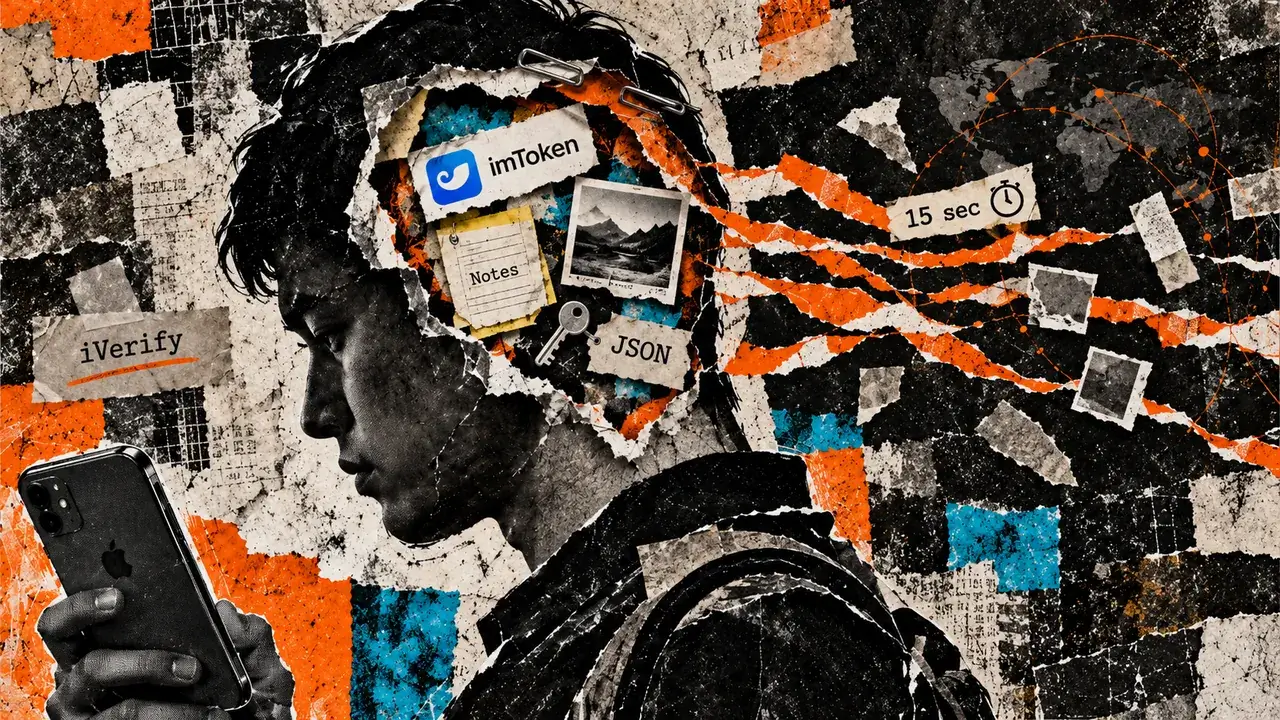
Security firm iVerify disclosed the malware, designated P7 DarkSword, on Oct. 8 after investigating an infection detected in August. The variant includes commands that specifically target cryptocurrency wallet apps and can collect passwords, photos, and personal information.
The discovery highlights an emerging risk for crypto holders who rely on mobile wallets: attackers who gain access to the underlying device could obtain sensitive information without exploiting a vulnerability in the wallet app itself.
How the spyware targets cryptocurrency wallets
According to iVerify’s technical…