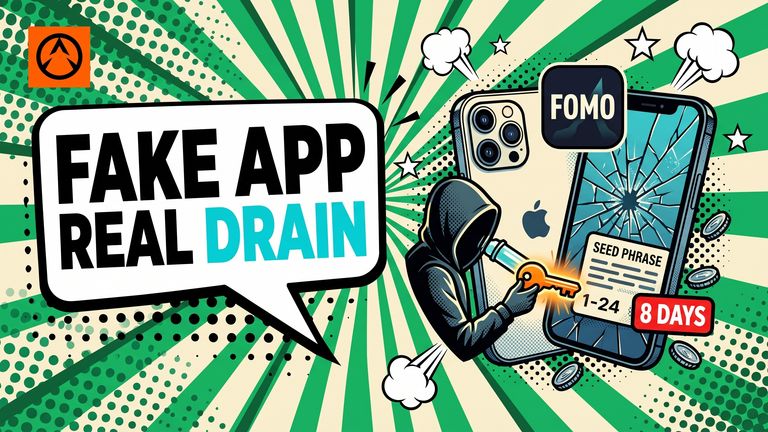
A malicious app called FOMO stayed on Apple’s App Store for 8 days, from September 9 to September 17, with crypto-draining malware on board, blockchain security firm SlowMist found. SlowMist’s chief information security officer, Shān Zhang, urged iPhone users to update to the latest iOS version after the discovery.
The app was promoted by crypto key opinion leaders and contained malware hidden in modules capable of stealing seed phrases and private keys. SlowMist’s analysts also flagged a separate wave of crypto-stealing malware spread through malicious Safari links exploiting the same iOS flaw.
How the drain worked
The FOMO modules exploited a memory-corruption flaw in WebKit and JavaScriptCore, the engine pair that powers Safari and…